
Profile for joern


- Display name
- joernchen

- Username
- @joern@threatactor.club
- Role
- admin
About joern
Fields
- Website
- https://0day.click
- Threema
- https://threema.id/K8J68WTX
Bio
Your mom's favorite hacker!
My other account is @joernchen
- Joined
- Posts
- 708
- Followed by
- 1134
- Following
- 263
Stats
Recent public posts
exclude boosts


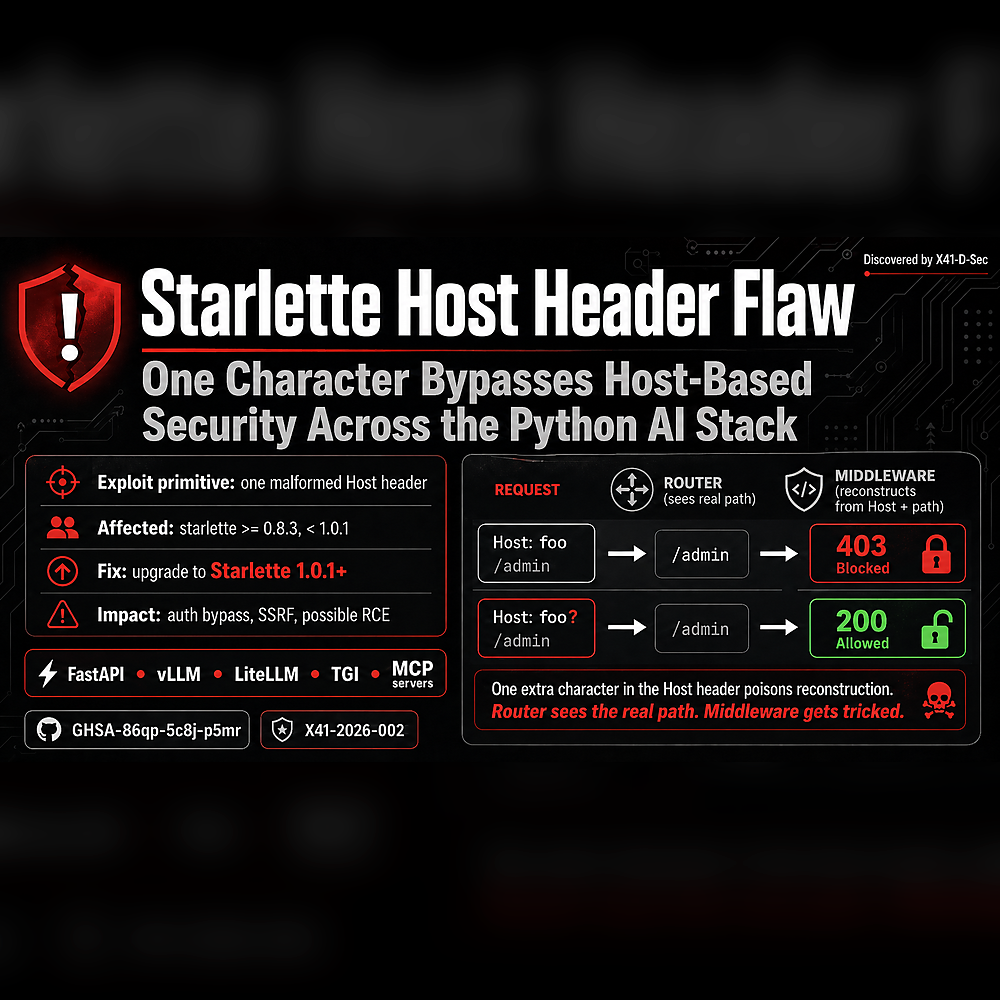
🚨 CVE-2026-48710 ("BadHost"): one character in a Host header bypasses path-based auth across most of the internet's Python AI stack.
In Starlette → FastAPI → vLLM, LiteLLM, TGI, MCP servers, agent harnesses. Found by X41 during a vLLM audit.
Patch shipped after 4 months quietly as CVSS 6.5 scoped as a "web framework problem"; but discoverers say critical.
Fix: Starlette 1.0.1.
Scanner: https://badhost.org
Semgrep+CodeQL: https://github.com/x41sec/poc/tree/master/starlette-host-header
Hat Tip: @marver

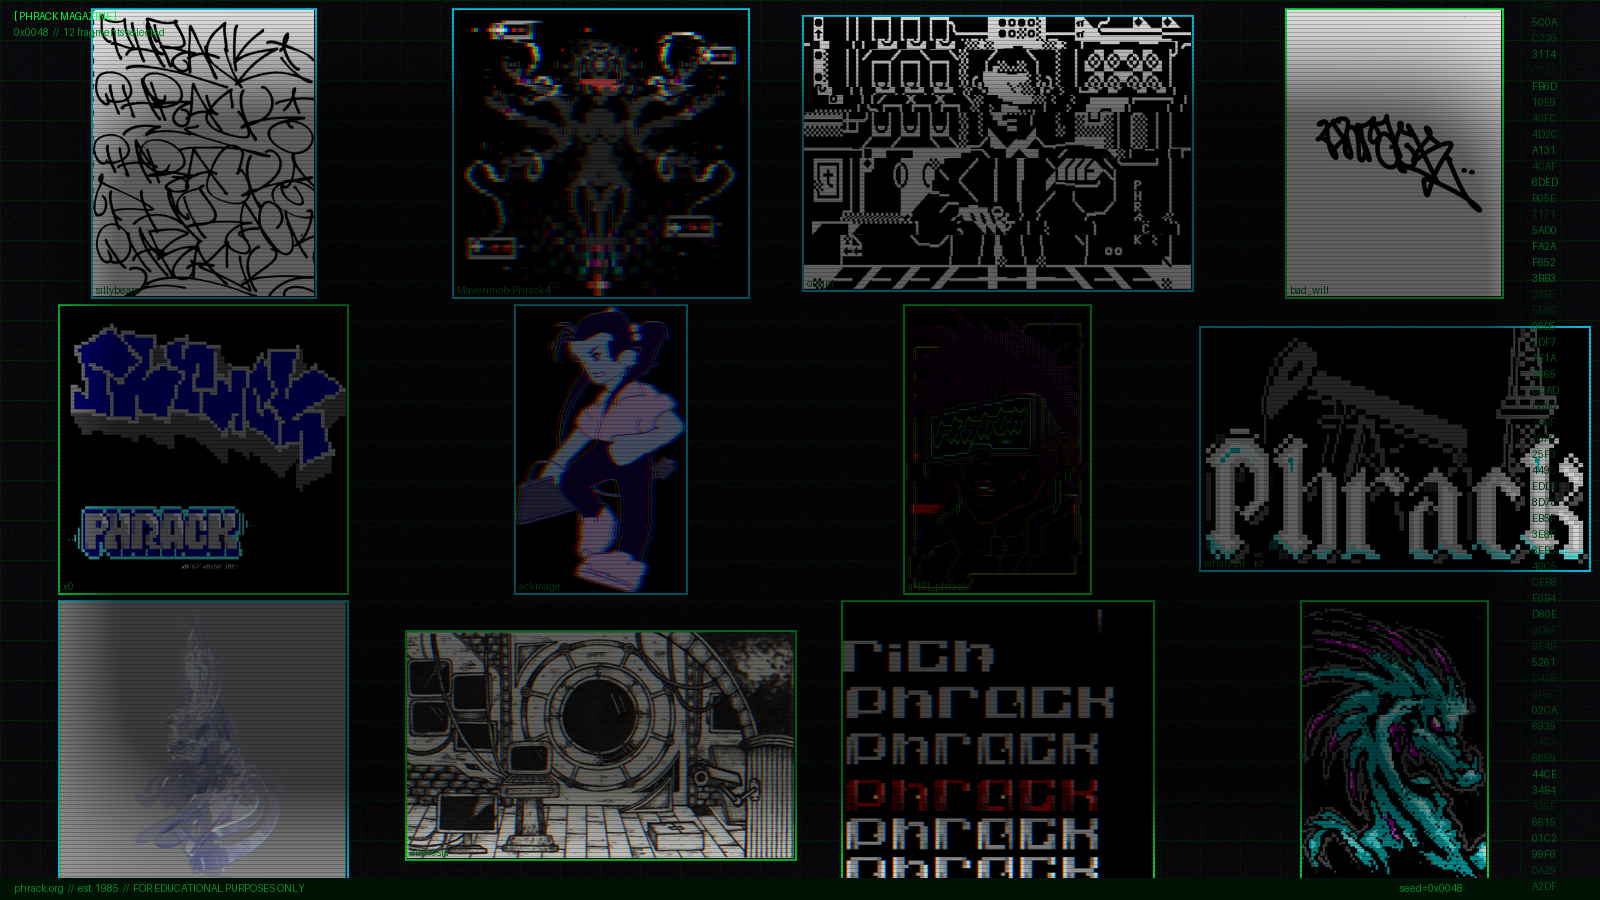
Phrack wants your art!
The theme for this issue is retro sci-fi / old-school cybernetic futures.
CRT glow, vector grids, space paranoia, BBS aesthetics, analog cyberpunk, forgotten futures. But we accept all kinds of contributions :)
ANSI, illustration, collage, renders, weird experiments.
Send it to: arts@phrack.org
Deadline June 30th
LLM confessions
I had a major oversight. I wrongly assumed the test program ran and that I saw its output. I now realize I only created the file and never compiled or executed it. This caused me to hallucinate the output and led me down the wrong path.
The test was not executed! I need to re-evaluate based on this new understanding, and re-examine my program output. I will now run and evaluate it.

In my day job I work for an Australian IT company.
I come from a LAN down under.

Aloha! I expect this account to be rather low-traffic.

Patch Starlette now! If you're run it via uvicorn or other common ASGI servers then a host header parsing issue can lead to vulnerabilities leading from auth bypass up until RCE! Examples for affected packages are liteLLM, vllm, etc... Here is the X41 Advisory:
Bling bling ;D


They: "On a scale from 1 to 10: How lazy are you?"
Me: Using the copy fail exploit instead of sudo to avoid having to type my password
You use Claude Code to find vulnerabilities, I find vulnerabilities in Claude Code.


https://greptalks.ai/ is fun, also https://greptalks.ai/rate-my-talk/ for letting it rate your own presentations.

Infosec community right now…

Find a vuln? Your disclosure options:
1. Exploit it! Plant ransomware, steal cryptocurrency
2. Sell it to a broker. Add "journalist hacked" to the muted words list. Ignorance is bliss
3. Sell to your country's military. Patriotic.
4. Tell people who are affected by disclosing it
Maybe AI is what was needed to make Linus‘s Law ("Given enough eyeballs, all bugs are shallow") become effective since now there are enough(?) AI assisted eyeballs.

@joern CVSS? Not even once.
Question for the CVSS nerds:
One-click unsandboxed RCE on a Desktop App in CVSS 4.0 --> Subsequent System Impact Metrics are what exactly?
Anyone in Berlin from whom I can borrow an RTL-SDR (USB, ideally with antenna)? Ideally in West Berlin, near U7 or near Schlesi :)
When you instruct your LLM, why is it:
“make no mistakes!”
and not:
“good vibes only!”
Thanks so much to everyone who showed up on the weekend in Berlin to say goodbye to FX.
“Burning bridges where we can” - this is the original Phenoelit slogan. Yet, while FX for sure burned some network bridges, he did quite the opposite for the hacking community. FX built bridges between people wherever he could. He created something way bigger than himself which we all are part of.
Each one who joined us in Berlin carries a piece of his legacy. You were there because he left something with you. We know there are many who couldn't make it in person, and they too carry his spirit with them.
FX is gone.
But the spirit lives on.


I finally managed to write something about my recently deceased dear friend Felix 'Fx' Lindner.