
Profile for joern


- Display name
- joernchen

- Username
- @joern@threatactor.club
- Role
- admin
About joern
Fields
- Website
- https://0day.click
- Threema
- https://threema.id/K8J68WTX
Bio
Your mom's favorite hacker!
My other account is @joernchen
- Joined
- Posts
- 724
- Followed by
- 1139
- Following
- 264
Stats
Recent public posts
exclude boosts


I heard last week that the physics teacher of the daughter of one of my colleagues told the daughter that girls who do their nails don’t do physics. Sigh.
So, here are the nails of an internationally leading particle physics professor. My nails.
Don’t believe the gatekeepers! #womeninSTEM
How many hours have you personally wasted by disassembling a binary file with the wrong CPU setting?

🔔CFP for #OffensiveCon26 is STILL open.
If you want a slot on one of the most technical offensive security stages out there, this is it.
We’re looking for real, original work: cutting-edge security research, novel exploit techniques, and deep technical investigations that actually move the field forward. Ready or not, the deadline is coming.
🗓️ CFP Deadline: 1 March 2026, 6:00 pm UTC
📬 Submit your talk: https://buff.ly/bPTM6wl
⏳ Last weeks. No extensions.
Katzen & Bass
Denkt dran Kinders:
Erst wenn der Subwoofer die Katze inhaliert, fickt der Bass richtig übel!


Last week I wondered when https://openinframap.org/ would be classified as terrorism - this week already we're a step further.
new year new meme
67 is so over. it’s time for 4️⃣ 5️⃣
For the Berlin peeps:
I’ll be playing some tunes tonight together with the amazing poco1oco, don’t miss out https://www.eschschloraque.de/vinyltrottel-02012026
Happy twenty twenty something, may it treat YOU well!

So the big thing in Bug Bounty now seems to be letting an LLM generate artificial PoCs for "issues" within a trust boundary.
Basically what's submitted as proof would be a snippet of code demonstrating a library "vulnerability" where all further context is left out.
Caffeine done like IDGAF, my 'Zero Fucks Given' cup with a double (maybe triple) Espresso Macchiato and some ice cold Club Mate.
¯\(ツ)/¯


@raptor @joern There is! https://downdetectorsdowndetector.com/ seems to be wrong though :(
Happy cloudflare is down day to those who celebrate

Stealth died 😢 A member of Team-Teso, Phrack staff, and many other groups. A true hacker—perhaps as true as a hacker can ever be. WE MISS YOU. 🩷
More: https://thc.org/404
<stealth> we had joy we had fun we had a rootshell on a sun.

If you're a #security person aka #infosec my employer is hiring. While most of the open positions are tied to a region, it is #allremote here.
https://about.gitlab.com/jobs/all-jobs/#security
If you're a #coder (mainly #Ruby, #golang, #RubyonRails, some #Python) there are open positions as well. Again, we're #allremote here.
Happy Friday


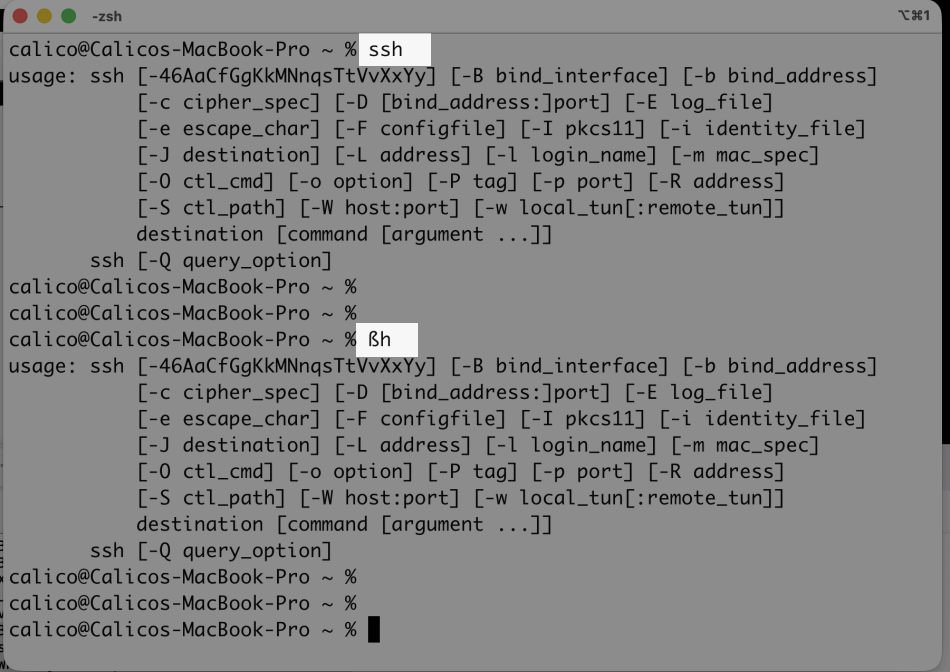
This MacOS (APFS?) quirk was mentioned at the pub last night, and I still cannot believe this actually works when I tried it myself

If you could go back and time and reverse ONE thing, which would it be?
i would be _so_ pissed https://joshua.hu/ai-slop-okta-nextjs-0auth-security-vulnerability
I’m slightly mad….
What stands in my way of having a nice vulnerability is the apparent inability of certain LLMs to emit \r (carriage return). For some reason they keep emitting \n (newline) instead.

@picofarad that reminds me of the time some corporate security engineer asked my team to build guardrails to guarantee the EICAR test virus can't escape onto the internal network 😂