
Profile for joern


- Display name
- joernchen

- Username
- @joern@threatactor.club
- Role
- admin
About joern
Fields
- Website
- https://0day.click
- Threema
- https://threema.id/K8J68WTX
Bio
Your mom's favorite hacker!
My other account is @joernchen
- Joined
- Posts
- 708
- Followed by
- 1134
- Following
- 263
Stats
Recent public posts
exclude boosts

For the Berlin peeps:
I’ll be playing some tunes tonight together with the amazing poco1oco, don’t miss out https://www.eschschloraque.de/vinyltrottel-02012026
Happy twenty twenty something, may it treat YOU well!

So the big thing in Bug Bounty now seems to be letting an LLM generate artificial PoCs for "issues" within a trust boundary.
Basically what's submitted as proof would be a snippet of code demonstrating a library "vulnerability" where all further context is left out.
Caffeine done like IDGAF, my 'Zero Fucks Given' cup with a double (maybe triple) Espresso Macchiato and some ice cold Club Mate.
¯\(ツ)/¯


@raptor @joern There is! https://downdetectorsdowndetector.com/ seems to be wrong though :(
Happy cloudflare is down day to those who celebrate

Stealth died 😢 A member of Team-Teso, Phrack staff, and many other groups. A true hacker—perhaps as true as a hacker can ever be. WE MISS YOU. 🩷
More: https://thc.org/404
<stealth> we had joy we had fun we had a rootshell on a sun.

If you're a #security person aka #infosec my employer is hiring. While most of the open positions are tied to a region, it is #allremote here.
https://about.gitlab.com/jobs/all-jobs/#security
If you're a #coder (mainly #Ruby, #golang, #RubyonRails, some #Python) there are open positions as well. Again, we're #allremote here.
Happy Friday


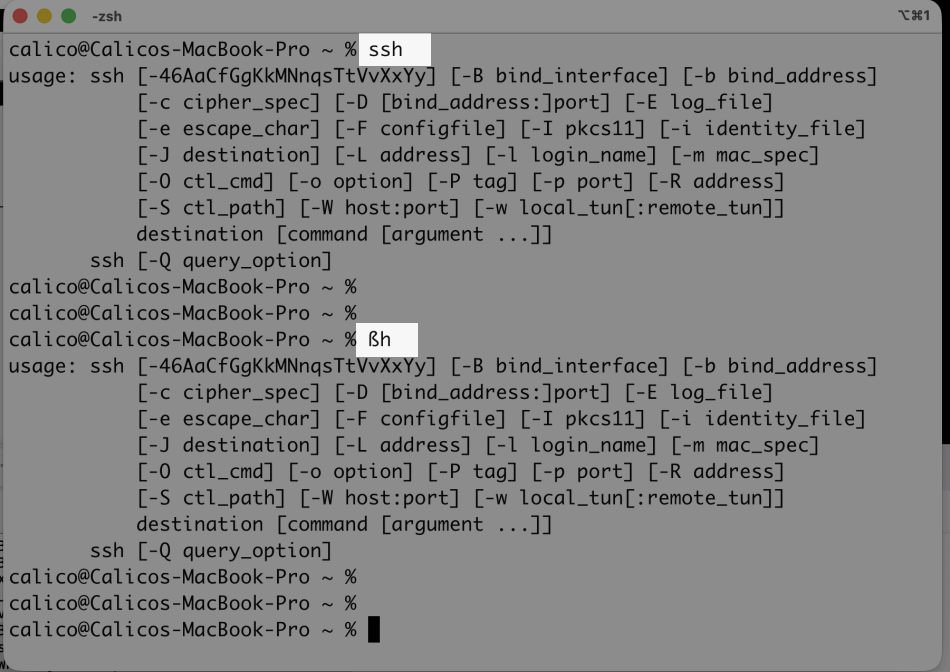
This MacOS (APFS?) quirk was mentioned at the pub last night, and I still cannot believe this actually works when I tried it myself

If you could go back and time and reverse ONE thing, which would it be?
i would be _so_ pissed https://joshua.hu/ai-slop-okta-nextjs-0auth-security-vulnerability
I’m slightly mad….
What stands in my way of having a nice vulnerability is the apparent inability of certain LLMs to emit \r (carriage return). For some reason they keep emitting \n (newline) instead.

@picofarad that reminds me of the time some corporate security engineer asked my team to build guardrails to guarantee the EICAR test virus can't escape onto the internal network 😂
This is today. Join us in Berlin / Stadtmitte :)
https://social.security.plumbing/@freddy/115535781812725548

Reversing public #security advisories has been a lot of fun lately. Here's an exploit I've built for CVE-2025-9501 that potentially affects 1+ million #WordPress installations:
I found myself posting this little comic at work A LOT currently.
It's really interesting, especially in the context of (agentic) AI, how features can be bugs or even vulnerabilities and vice versa, depending on whom you ask about it. It's always the context which matters and a lot is personal preference/risk appetite of whoever is using the 'feature'.
I tend to advocate for secure defaults with an option to let anyone choose if they want to take the risk of e.g. AI 'yolo' mode.

So I just met someone in person a few days ago. They said: "Oooh you're busy looking into AI stuff lately? That's good so you wont bother $THING with vuln reports! :P"
Guess where I just found a nice vuln 