Profile for joern


- Display name
- joernchen

- Username
- @joern@threatactor.club
- Role
- admin
About joern
Fields
- Website
- https://0day.click
- Threema
- https://threema.id/K8J68WTX
Bio
Your mom's favorite hacker!
My other account is @joernchen
- Joined
- Posts
- 708
- Followed by
- 1134
- Following
- 263
Stats
Recent public posts
exclude boosts

I found myself posting this little comic at work A LOT currently.
It's really interesting, especially in the context of (agentic) AI, how features can be bugs or even vulnerabilities and vice versa, depending on whom you ask about it. It's always the context which matters and a lot is personal preference/risk appetite of whoever is using the 'feature'.
I tend to advocate for secure defaults with an option to let anyone choose if they want to take the risk of e.g. AI 'yolo' mode.


So I just met someone in person a few days ago. They said: "Oooh you're busy looking into AI stuff lately? That's good so you wont bother $THING with vuln reports! :P"
Guess where I just found a nice vuln 
I found a thing (RCE) in langgraph. ;D
https://github.com/langchain-ai/langgraph/security/advisories/GHSA-wwqv-p2pp-99h5

As an extra layer of protection against the npm worm currently circulating, I've uninstalled node on my dev system and cooked up this node-container-exec script to use instead. My node and npm commands now exec through node-container-exec.
It mostly transparently runs node stuff in an ephemeral node:24-trixie-slim container with podman. By default it only read-only bind mounts top-level files and directories tracked by git to avoid accidental secret leakage into the container. You can override what gets bind mounted by setting the NODE_CONTAINER_BIND and NODE_CONTAINER_BIND_RO env vars. Use direnv to do this on a per-project basis.
No, containers do not provide flawless security, but all of the npm malware I've seen so far is just script kiddy shit that a container would adequately protect against.
You might find the script useful too: https://gist.github.com/haileys/a4eb8a7ec78f5dc5ab57d4b430fa1904
Want to hack AI things with me?
ID theft is real!!

I call the slides done, see you tomorrow at Nullcon!


Took way too long to get this one released https://x41-dsec.de/lab/advisories/x41-2024-004-Medico/
Ich muss sagen ich bin schon ein bisschen beeindruckt wie smooth eine Onlinezulassung für ein Kfz läuft, ABER wenn ein einfaches & in den Eingabedaten so eine Fehlermeldung auslöst triggert mich das ein bisschen zu sehr ;).
Ich hab dann aber mal nicht an dem Ast gesägt auf dem ich saß.


TIL: Vodafone schickt jetzt bei VoLTE calls fragwürdiger Quelle einen Warntext in der Callerid mit:

A quick reminder: dueling URL parsers is a path to pain and sorrow.
(blogged two years ago)
https://daniel.haxx.se/blog/2022/01/10/dont-mix-url-parsers/

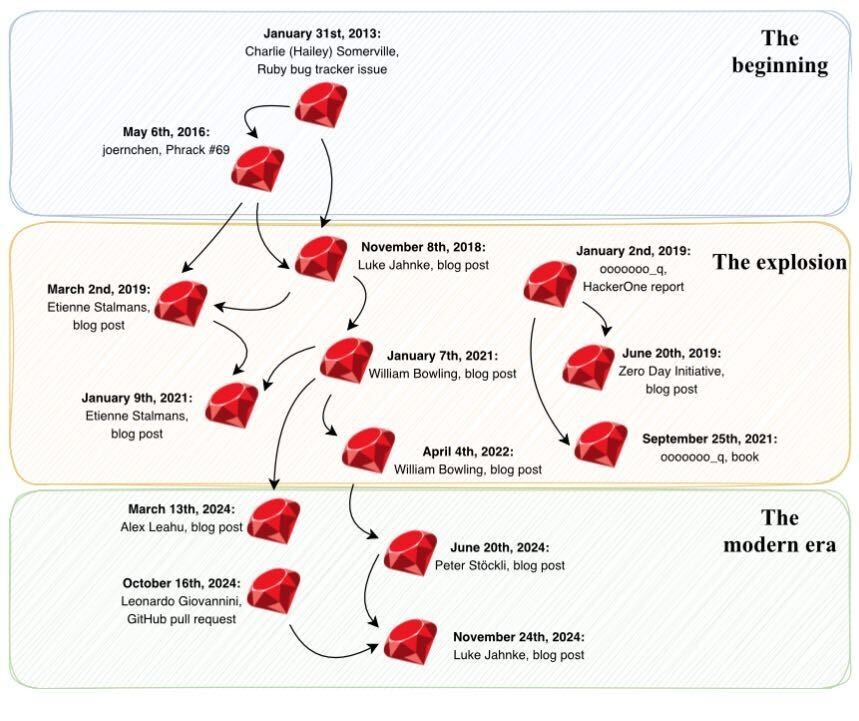
Ruby's Marshal deserialization has been broken for over a decade, and patches don't solve the fundamental issue. Read our full analysis of 11 years of Ruby deserialization exploits and why fundamental change is needed: https://blog.trailofbits.com/2025/08/20/marshal-madness-a-brief-history-of-ruby-deserialization-exploits/

I’m looking for audio or videos from early Dutch Hacker cons, does anyone know if they exist for Hacking In Progress (HIP97), Hacking at the End of the Universe (HEU93), or Galactic Hacker Party (GHP89) ?
Today I have a more serious topic than usual, please consider reposting for reach:
My wife and I are urgently looking for a specialist in neuropediatrics or a similar field for our autistic child with a diagnosed, but not further specified, movement disorder (myoclonus and/or spasms) to finally find a cause and, above all, an effective therapy. The symptoms are bothering our son ever since he’s born, now for more than nine years, seriously affecting his sleep. The usual processes and medical contact points have failed us unfortunately and he seems stuck in this condition.
We’re based in Berlin, Germany but really any contact with a specialist who would be willing to take on this case we’d be grateful for!
To reach use you can DM me or contact us via Email at unclear.condition@gmail.com

We're still looking for submissions for German OWASP Day in Düsseldorf. The event is on the 26th of November and the CfP closes this week. https://god.owasp.de/2025/en/cfp.html :)

https://scrapco.de/dataslate/phrack/
(Will probably update when 72 comes out)


hey guys isn't it soo annoying when you're using an encrypted messaging app and it tells you "could not decrypt" haha
good news: we're working hard on making this illegal. in a way